Nuxt Middleware Explained — Auth, Redirects & Route Guards Deep Dive
Nuxt middleware runs before a page loads so you can check auth, redirect users, or block a route — on the server for the first hit and in the browser on later navigations.
Quick Answer
Nuxt middleware is code that runs before a page finishes navigating. Use it to check login, redirect guests, rewrite paths, or stop a navigation early. On the first visit it can run during SSR; on later client clicks it runs in the browser. Put “gatekeeper” logic here — not charts, not DOM work, and not secrets that belong only on the server API.
Quick Facts
Topic: Nuxt middleware (route guards)
Category: Nuxt.js / Routing & Auth
Table of Contents
- What Is Nuxt Middleware?
- Why It Matters
- How It Works
- Step-by-Step Guide
- Real Example
- Pros & Cons
- Best Practices
- Common Mistakes
- FAQs
- Key Takeaways
What Is Nuxt Middleware?
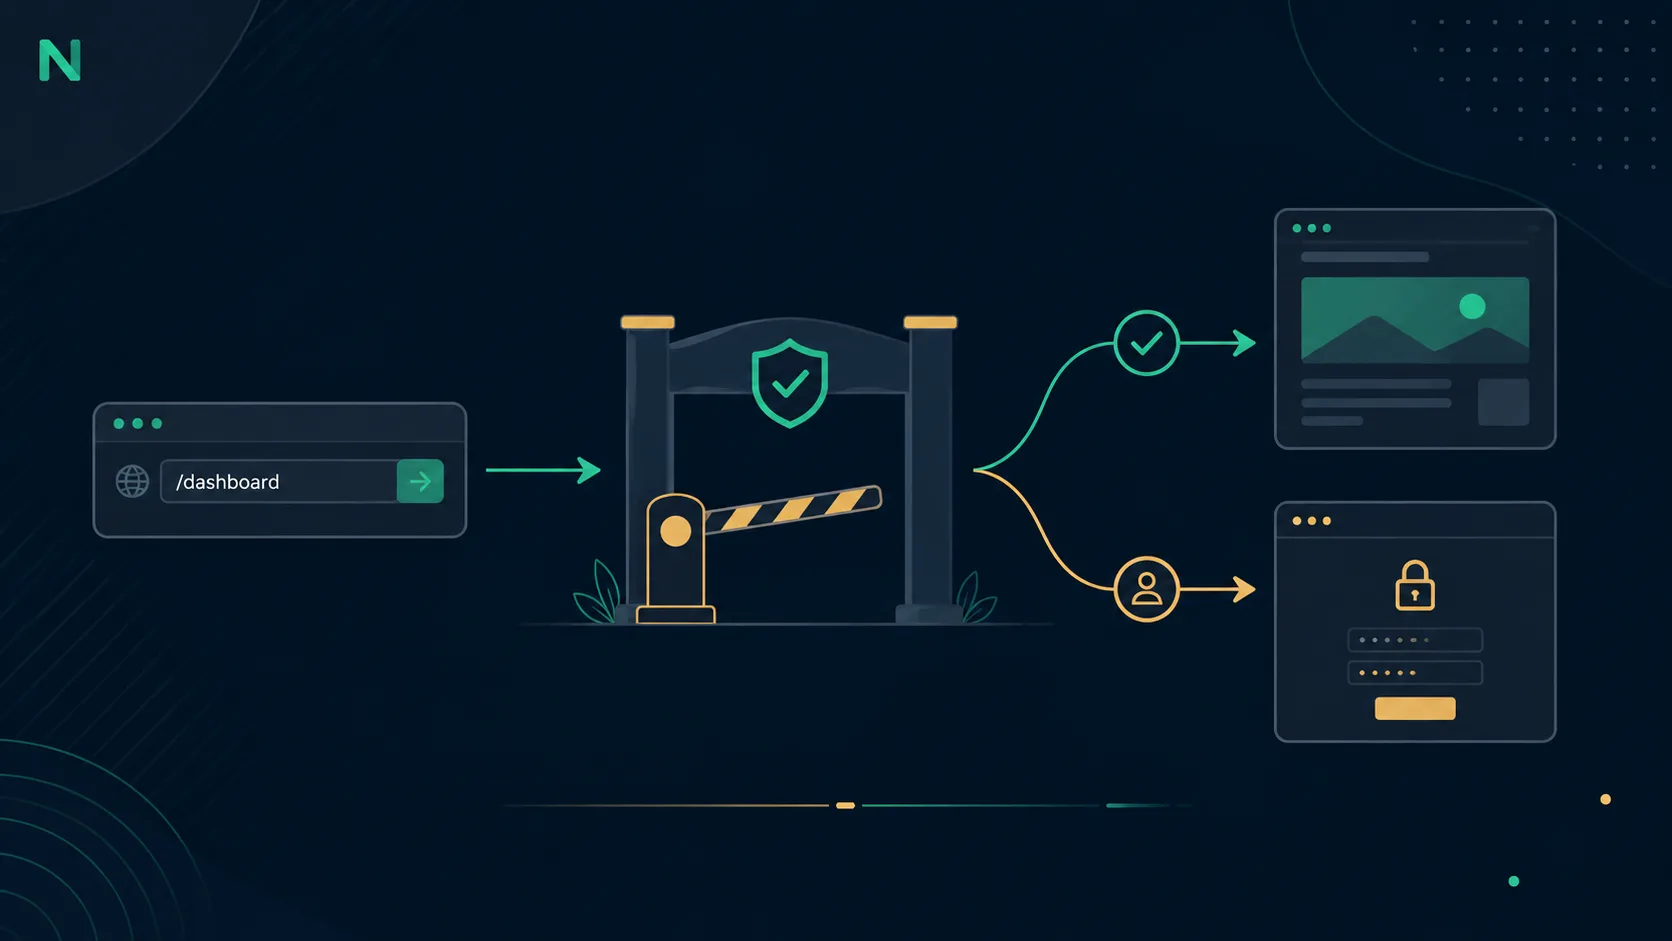
Think of middleware as a security/checkpoint guard at the door of a page. The visitor asks for /admin. Before the admin UI mounts, Nuxt runs your middleware. The guard can say “go in,” “go to login,” or “stop.”
In Nuxt 3/4 this usually means route middleware via defineNuxtRouteMiddleware in the middleware/ folder (or inline on a page). That is different from Nitro server middleware under server/middleware, which runs on every API/server request. This article focuses on route middleware — the one you use for pages, layouts, and SPA-style navigations — and calls out server middleware only where people mix them up.
If you already read Nuxt Lifecycle Explained, middleware sits in that timeline after the route is matched and before the page is fully shown with its final navigation result.
Why It Matters
- Auth that runs early — users never flash a protected page for a second before redirect.
- One place for rules — “must be logged in,” “must be admin,” “must finish onboarding” stay out of messy page templates.
- SSR-aware gates — first HTML request can redirect on the server, which is better for SEO and security UX.
- Consistent client navigations — the same rules apply when users click
NuxtLinkinside the app. - Cleaner pages — pages focus on UI and data; middleware focuses on access.
How It Works
Middleware is part of Nuxt’s navigation pipeline. Simplified flow:
- Route match — Nuxt knows which page (and layout) you want.
- Middleware list builds — global → named (from page/layout meta) → any inline middleware, in a defined order.
- Each middleware runs — you receive
toandfromroute objects. - You return a decision — nothing (continue),
navigateTo(...)(redirect), orabortNavigation(...)(cancel). - Page continues — only if every middleware allows it; then data fetching / render continue in the lifecycle.
Important mental model:
- First load / refresh — middleware can run on the server (SSR). No
window, nolocalStorageunless you guard withimport.meta.client. - In-app navigation — middleware runs on the client.
- Same code file — often one middleware must be safe in both environments.
Types you’ll use:
- Global — filename ends with
.global.ts(example:middleware/auth.global.ts). Runs on every route change. - Named —
middleware/auth.ts→ use asdefinePageMeta({ middleware: 'auth' }). - Inline — anonymous function in
definePageMeta({ middleware: [defineNuxtRouteMiddleware(...)] })for one-off rules (keep rare).
Route middleware vs server middleware:
- Route middleware — pages/layouts, auth redirects, A/B routing UX.
- Server middleware (
server/middleware) — every HTTP hit to Nitro (APIs, headers, logging). Do not put Vue page redirects only there and expect identical SPA behavior.
Step-by-Step Guide
Step 1: Create a named middleware
Add middleware/auth.ts:
export default defineNuxtRouteMiddleware((to) => {
  const session = useSupabaseSession() // example — use your auth source

  if (!session.value && to.path.startsWith('/admin')) {
    return navigateTo('/admin/login')
  }
})
Keep the function small: read state → decide → return redirect or nothing.
Step 2: Attach it to pages (or make it global)
On a protected page:
definePageMeta({
  middleware: 'auth',
})
Multiple middlewares (order matters — left to right / array order):
definePageMeta({
  middleware: ['auth', 'onboarding'],
})
For rules that must run everywhere, rename to auth.global.ts. Global middleware is powerful — and easy to overuse. Prefer named middleware when only a few routes need the gate.
Step 3: Redirect and abort the Nuxt way
return navigateTo('/login')— send the user elsewhere. Preferreturnso navigation waits on it.return navigateTo('/login', { replace: true, redirectCode: 302 })— useful on SSR redirects.return abortNavigation()orabortNavigation(error)— cancel this navigation (stay / show error depending on context).
Avoid raw window.location = ... inside middleware unless you intentionally want a hard browser reload.
Step 4: Make it SSR-safe
Ask: “Will this run on the server on first paint?”
- Read cookies / server-known session — good on SSR.
- Read
localStorageonly — breaks or lies on SSR (empty on server, filled on client → hydration/auth flicker).
Pattern:
export default defineNuxtRouteMiddleware((to) => {
  if (import.meta.server) {
    // cookie / server session check
  }
  if (import.meta.client) {
    // optional client-only enrichment
  }
})
For real security, never rely on middleware alone: protect APIs and server routes too. Middleware is a UX + soft gate; server auth is the hard gate.
Step 5: Pass context with route meta (optional but deep)
You can mark pages and read flags in middleware:
// page
definePageMeta({
  middleware: 'auth',
  roles: ['admin'],
})

// middleware
export default defineNuxtRouteMiddleware((to) => {
  const roles = to.meta.roles as string[] | undefined
  // compare to user roles…
})
This keeps one middleware reusable across many pages with different rules.
Step 6: Test both first load and in-app clicks
- Open protected URL in a new tab (SSR path).
- Click from a public page to the protected page (client path).
- Confirm no “flash of admin UI,” and redirect target is correct both times.
Real-World Example
Portfolio admin area (same pattern as many Nuxt + Supabase apps, including setups like this site’s blog admin):
- Public pages:
/,/blog,/about— no auth middleware. /admin/**— must be logged in./admin/login— guests allowed; logged-in users maybe redirect to dashboard.
Named middleware sketch:
export default defineNuxtRouteMiddleware((to) => {
  const session = useSupabaseSession()
  const isAdmin = to.path.startsWith('/admin')
  const isLogin = to.path === '/admin/login'

  if (isAdmin && !isLogin && !session.value) {
    return navigateTo('/admin/login')
  }

  if (isLogin && session.value) {
    return navigateTo('/admin')
  }
})
Before: each admin page checked auth in onMounted → guests saw a blank admin shell, then bounced.
After: middleware redirects before the protected page becomes the active route — cleaner and closer to how the Nuxt lifecycle expects gates to run.
Pros & Cons
Advantages
- Early, consistent access control across SSR and client navigations
- Reusable rules via named middleware +
definePageMeta - Keeps pages thinner and easier to maintain
- Works naturally with
navigateToredirects
Disadvantages
- Easy to write browser-only code that breaks on first SSR request
- Global middleware can slow or complicate every navigation if overused
- Not a replacement for API/server authorization
- Debugging order (global + many named) takes care
Best Practices
- Named over global unless the rule truly applies to almost all routes.
- SSR-safe session source (cookies / server-aware auth), not only
localStorage. - Always
return navigateTo(...)so Nuxt waits on the redirect. - Keep middleware pure and short — no heavy data fetching; fetch in the page with
useAsyncData/useFetch. - Protect APIs separately — middleware is necessary but not sufficient for security.
- Log decisions in development — path, user present?, redirect target.
- Align with lifecycle knowledge — gates early, DOM work in
onMounted(see lifecycle guide).
Common Mistakes
- Using
localStorageas the only auth check → Fix: cookie/session that exists on SSR, or accept client-only apps and live with first-paint limits. - Calling
navigateTowithoutreturn→ Fix:return navigateTo(...). - Putting secrets or DB logic in route middleware → Fix: call a server API / use server routes; keep client-safe decisions in middleware.
- Auth only in
onMounted→ Fix: move the gate to middleware to avoid UI flash. - One giant
.global.tsfor everything → Fix: split named middlewares; attach per page/layout. - Confusing
server/middlewarewith route middleware → Fix: use route middleware for page guards; server middleware for HTTP-level concerns. - Assuming middleware never runs on the server → Fix: write isomorphic, environment-aware code.
Frequently Asked Questions
What is Nuxt middleware?
It is a function that runs before a route navigation completes. You use it to allow the page, redirect the user, or abort the navigation — commonly for authentication and access control.
How do I add auth middleware in Nuxt?
Create middleware/auth.ts with defineNuxtRouteMiddleware, redirect when there is no session, then set definePageMeta({ middleware: 'auth' }) on protected pages — or use auth.global.ts if almost every route needs it.
Nuxt middleware vs Vue Router navigation guards?
Conceptually similar (run before entering a route). Nuxt wraps this with file-based middleware, definePageMeta, SSR execution on first load, and helpers like navigateTo. You usually write Nuxt middleware instead of hand-wiring Vue Router guards.
Is Nuxt middleware worth it?
Yes, whenever you have protected routes, onboarding steps, or locale/role gates. It prevents UI flash, centralizes rules, and fits SSR. For a public-only brochure site with zero gated pages, you may not need it.
Does Nuxt middleware run on the server?
It can — especially on the first request with SSR enabled. Later client-side navigations run it in the browser. Write middleware that works in both places unless you intentionally mark client-only behavior.
Route middleware vs server middleware in Nuxt?
Route middleware guards pages during navigation. Server middleware in server/middleware runs on Nitro HTTP requests. Use both when needed, but don’t mix their jobs.
Summary
Nuxt middleware is your route checkpoint: it decides who may enter a page before the UI settles. Master named vs global, SSR-safe session checks, and correct navigateTo/abortNavigation usage, and auth UX becomes predictable.
Keep middleware thin, pages focused on content, and APIs properly protected. That split matches how Nuxt’s navigation and lifecycle are designed to work together.
Next step: add one named auth middleware, protect a single admin page, and test both hard refresh and in-app navigation. Then expand with roles via to.meta.
Key Takeaways
- Middleware runs before the page navigation completes — ideal for auth and redirects.
- Use named middleware by default; reserve
.globalfor truly app-wide rules. - First load may run on the server — avoid browser-only APIs without guards.
- Always
return navigateTo(...); don’t treat middleware as full API security. - Pair this with the Nuxt lifecycle mental model: gates early, DOM later.
Comments
0 comments · new ones appear after approval
No comments yet. Be the first to share your thoughts.
Leave a comment
Your comment will be reviewed before it appears.